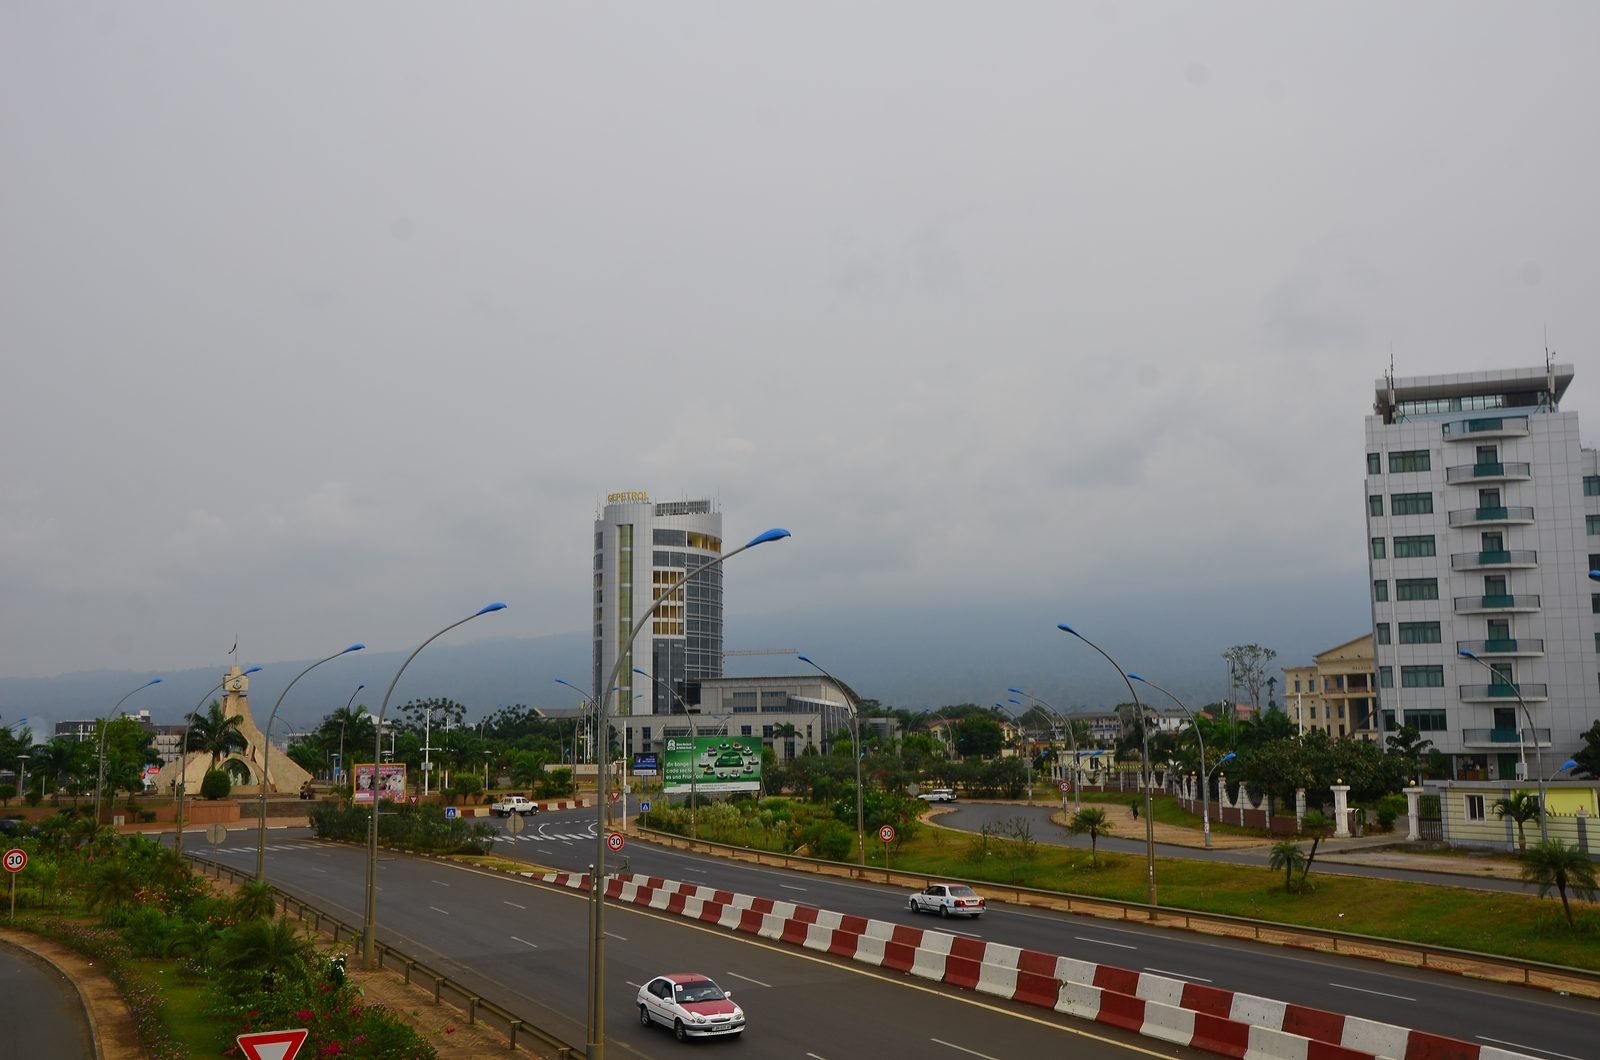
The African Union Convention on Cyber Security and Personal Data Protection, known as the Malabo Convention, is Africa’s main continental treaty on data protection, electronic transactions and cybercrime. Adopted in Malabo, Equatorial Guinea, in June 2014, it entered into force in June 2023 after reaching the required 15 ratifications.
What the Convention covers
1. Electronic transactions
Rules to build trust in e-commerce, including obligations on providers of online goods and services, recognition of electronic contracts and electronic signatures, and requirements around electronic advertising.
2. Personal data protection
Principles for processing personal data, such as consent and legitimacy, purpose limitation, accuracy, transparency, confidentiality and security, along with individuals’ rights to information, access, objection and correction. It calls on each state party to set up an independent national data protection authority.
3. Cybersecurity and cybercrime
Obligations to develop national cybersecurity policies and strategies, establish computer emergency response teams, criminalise offences such as unauthorised access to computer systems and data interference, and cooperate internationally on cybercrime.
Why it took so long to come into force
Ratification was slow for several reasons: many states already had or preferred their own national laws, some provisions were seen as outdated as technology moved on, and ratification competed with other priorities. It took about nine years to reach 15 ratifications.
What it means in practice
- The Convention binds only the states that have ratified it
- Its rules must generally be implemented through national legislation
- It provides a common reference point, encouraging harmonised approaches to data protection and cybercrime across Africa
- It supports cross-border cooperation between national authorities
Criticisms and limitations
- Some definitions and provisions were drafted before cloud computing, AI and modern data flows became widespread
- Rights groups have raised concerns that some cybercrime provisions could be used to restrict freedom of expression if implemented without safeguards
- Enforcement depends on national institutions, which vary in capacity
How it fits with other frameworks
- National laws: such as Nigeria’s NDPA, Kenya’s Data Protection Act and South Africa’s POPIA; see Data Protection Laws in Africa
- AU Data Policy Framework (2022): guidance for harmonising data governance and enabling data flows
- AfCFTA Digital Trade Protocol: trade rules covering cross-border data, e-commerce and digital payments
- Regional instruments: such as ECOWAS’s supplementary act on personal data protection
- The Budapest Convention on Cybercrime: a Council of Europe treaty that some African states have also joined
Why businesses should care
For companies operating across African markets, the trend towards harmonised data protection and cybersecurity rules means compliance expectations are rising everywhere. Building strong privacy and security practices now, as described in our cybersecurity guide, prepares you for stricter enforcement.
Back to our guide to tech policy in Africa.